Cloud Solutions
AWS and Azure architecture designed for your workload — secure by default, cost-optimised and built to scale without manual intervention.
Sound familiar?
- Downtime is discovered by customers before the team notices.
- The infrastructure is known by one person, and they are busy.
- Deployments are manual, and every release is a nervous afternoon.
That is the work this service exists for — scoped up front, delivered in clear milestones, with a fixed estimate before anything starts.
What we build
Cloud architecture design
Infrastructure designed for your workload — not a copy-paste setup that wastes money on over-provisioned resources.
Migration to cloud
We move existing infrastructure to AWS or Azure with minimal downtime and no data loss.
Security and compliance
VPCs, IAM policies, encryption and logging configured so your environment is secure by default.
Cost optimisation
Right-sized instances, reserved capacity and auto-scaling so you pay for what you use.
Why DevFuture
Products we've built and shipped
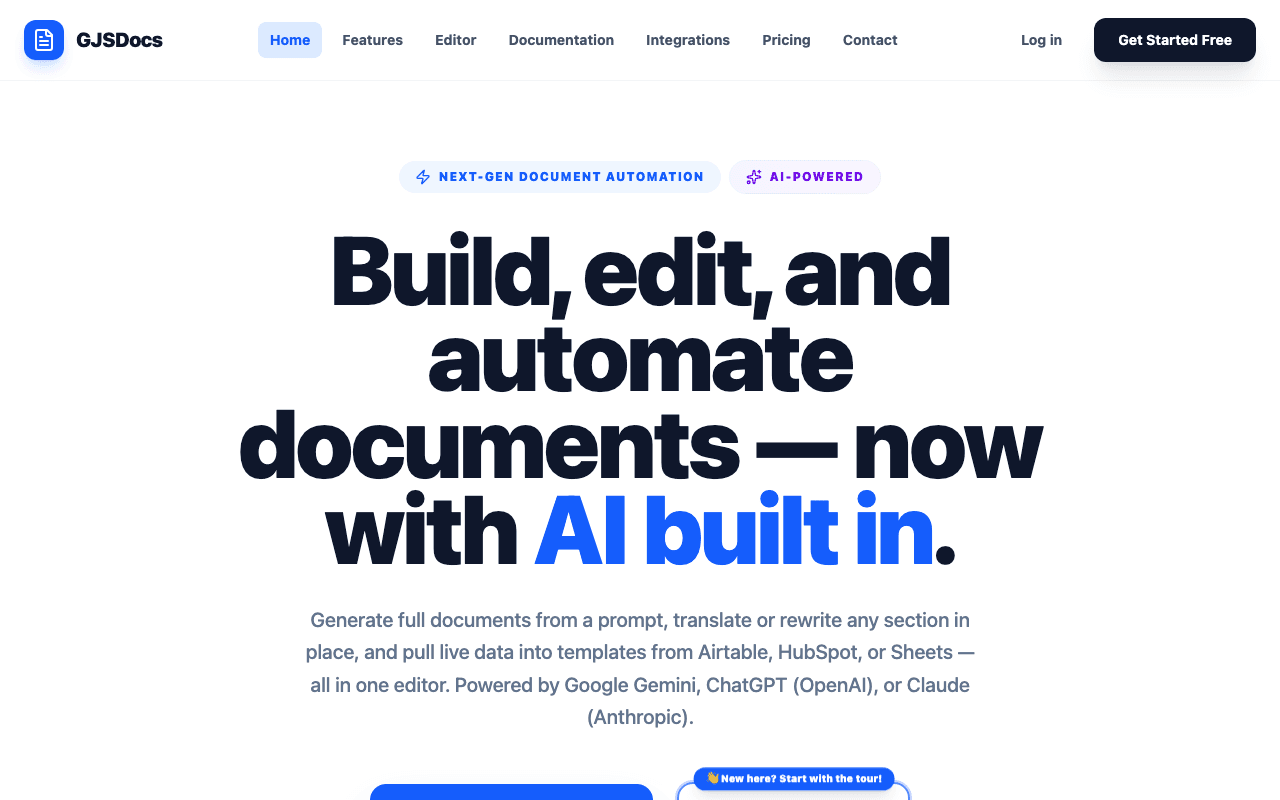
GJSDocs
AI-powered document automation — generate invoices, contracts and reports from templates merged with live data (Airtable, HubSpot, Sheets), with PDF/DOCX/HTML export and a full REST API.
Case study →Open live ↗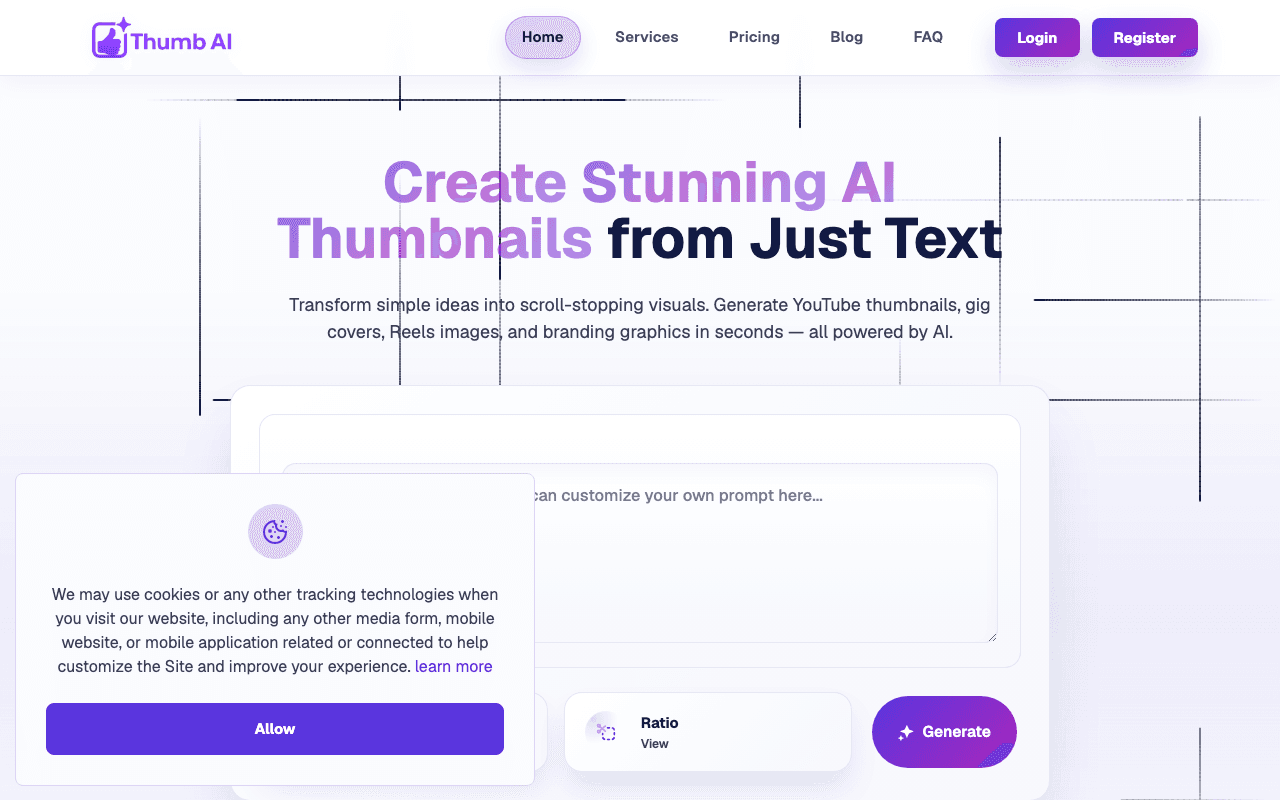
ThumbAI
AI thumbnail and cover generator that turns a text prompt into platform-ready visuals for YouTube, Instagram, TikTok and freelance marketplaces in seconds.
Case study →Open live ↗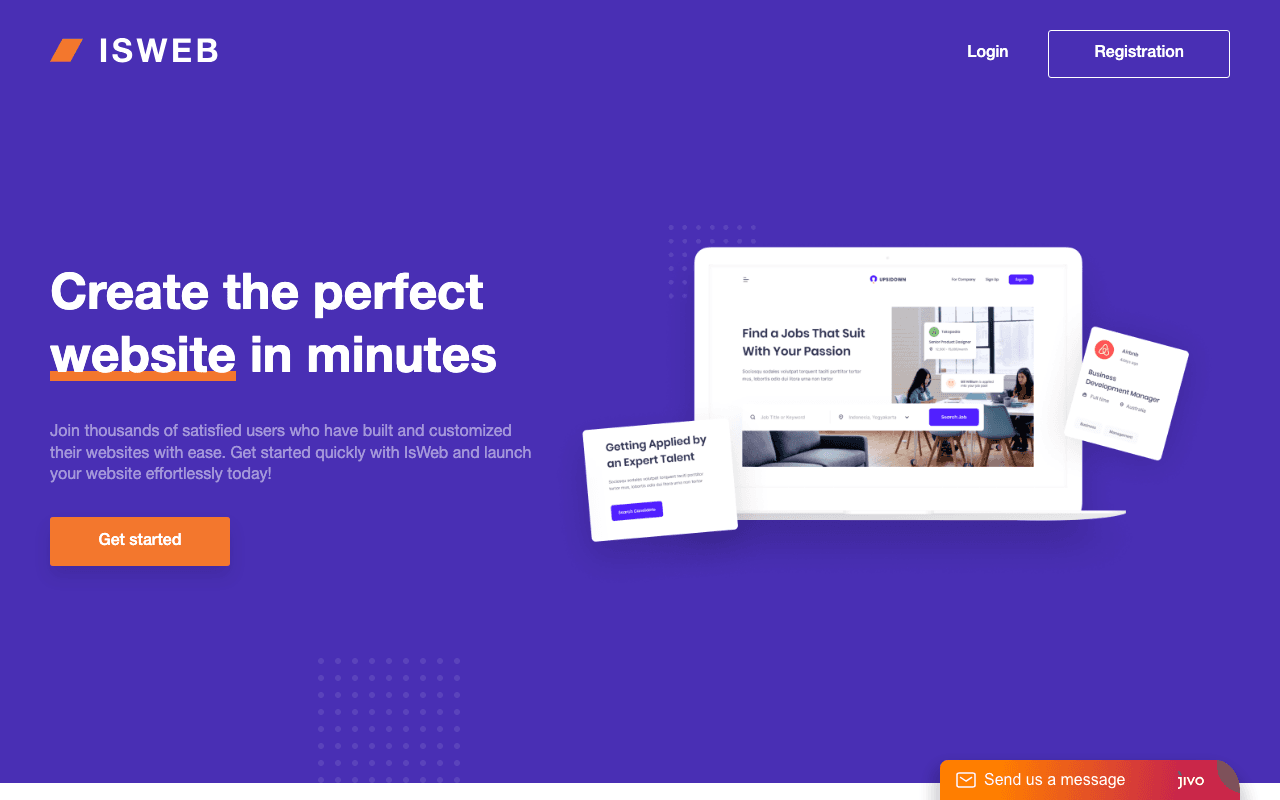
IsWeb
No-code drag-and-drop website builder with built-in domain registration and SEO tooling, launching responsive sites in a three-step setup.
Case study →Open live ↗How we work
Assessment
We assess your current infrastructure, workloads and requirements before recommending any cloud architecture.
Design
We design the target architecture with costs, tradeoffs and migration path documented and agreed.
Migrate
We execute the migration in stages, validating each step before moving to the next.
Optimise
Post-migration we monitor costs, performance and security and adjust over the first 90 days.
Architecture Before Infrastructure
Most cloud problems are not really cloud problems — they are architecture decisions made in a hurry that nobody revisited. A lift-and-shift of a few VMs onto AWS often costs more than the office servers it replaced, because the workload was never redesigned for what the cloud actually does well. We start with the workload, not the provider: what has to scale, what has to stay available, where the data lives, and what failure modes you can tolerate.
From there we design a target architecture and put the tradeoffs on the table — managed services versus self-hosted, single region versus multi-region, the cost and complexity each choice carries. You get a documented plan and a migration path before anyone touches a console, so the build is a known quantity rather than a series of surprises.
AWS, Azure and GCP
We work primarily across AWS and Azure, with GCP where it fits. AWS tends to win on breadth and on compute-heavy or data-heavy workloads; Azure is the natural choice when you are already invested in Microsoft identity, licensing and tooling; GCP earns its place for data and analytics-led platforms. The right answer depends on your existing stack and team, which is why we recommend rather than default.
Whichever provider, the building blocks are consistent: properly segmented networking with VPCs or VNets and private subnets, identity and access kept least-privilege, managed databases over hand-rolled ones where they fit, and serverless or container compute chosen to match the traffic shape rather than habit.
Infrastructure as Code, Security and Cost Control
Everything we provision is defined in Terraform, so the environment is reproducible, version-controlled and reviewable rather than a hand-clicked configuration nobody can recreate after the person who built it leaves. Staging and production are described by the same code with different variables, which is what keeps the two environments honestly in sync.
Security is built in from the start, not bolted on after an audit. Encryption at rest and in transit, scoped IAM roles, centralised logging and audit trails, secrets kept out of code, and sensible network boundaries are the baseline. Cost control runs alongside it: right-sized instances, autoscaling, reserved or savings-plan capacity for steady workloads, and lifecycle policies on storage so spend tracks usage instead of drifting upward unnoticed.
- Terraform-defined infrastructure that is reproducible and reviewable
- VPC or VNet segmentation with private subnets and least-privilege IAM
- Encryption at rest and in transit, with centralised audit logging
- Autoscaling and right-sized compute matched to real traffic
- Reserved capacity and savings plans for predictable workloads
- Cost dashboards and budget alerts so spend never drifts silently
Migration, Timeline and Fit
Migrations run in stages, not big-bang. We validate each workload in the new environment before cutting traffic over, keep a rollback path open, and schedule the riskier cutovers for low-traffic windows. A straightforward migration of a handful of services is usually a matter of weeks; a larger estate with databases and stateful systems is phased over a couple of months with the highest-value, lowest-risk pieces moved first.
This is the right work for teams outgrowing on-premise hardware, paying too much on a poorly configured cloud account, or needing reliability and scale they cannot get from a single server. It is not the right time if you are a very early-stage product still finding fit — a managed platform like a PaaS or a single well-run instance will serve you better until the workload justifies real architecture, and we will tell you when that line has not been crossed yet.
Technology
- AWS
- Docker
- Vercel
- CI/CD pipelines
- Monitoring & alerting
Cloud Solutions by location
Tell us what you need built
You'll get a written, fixed-scope estimate within 24 hours — and if we're not the right fit for it, we'll say so.